Last checked: 21 Oct 2026. Product facts come from Cursor's own documentation, help centre, Cursor Learn guide, pricing page and terms, and the research findings come from the published studies linked where they appear.
Last updated: 21 Oct 2026.
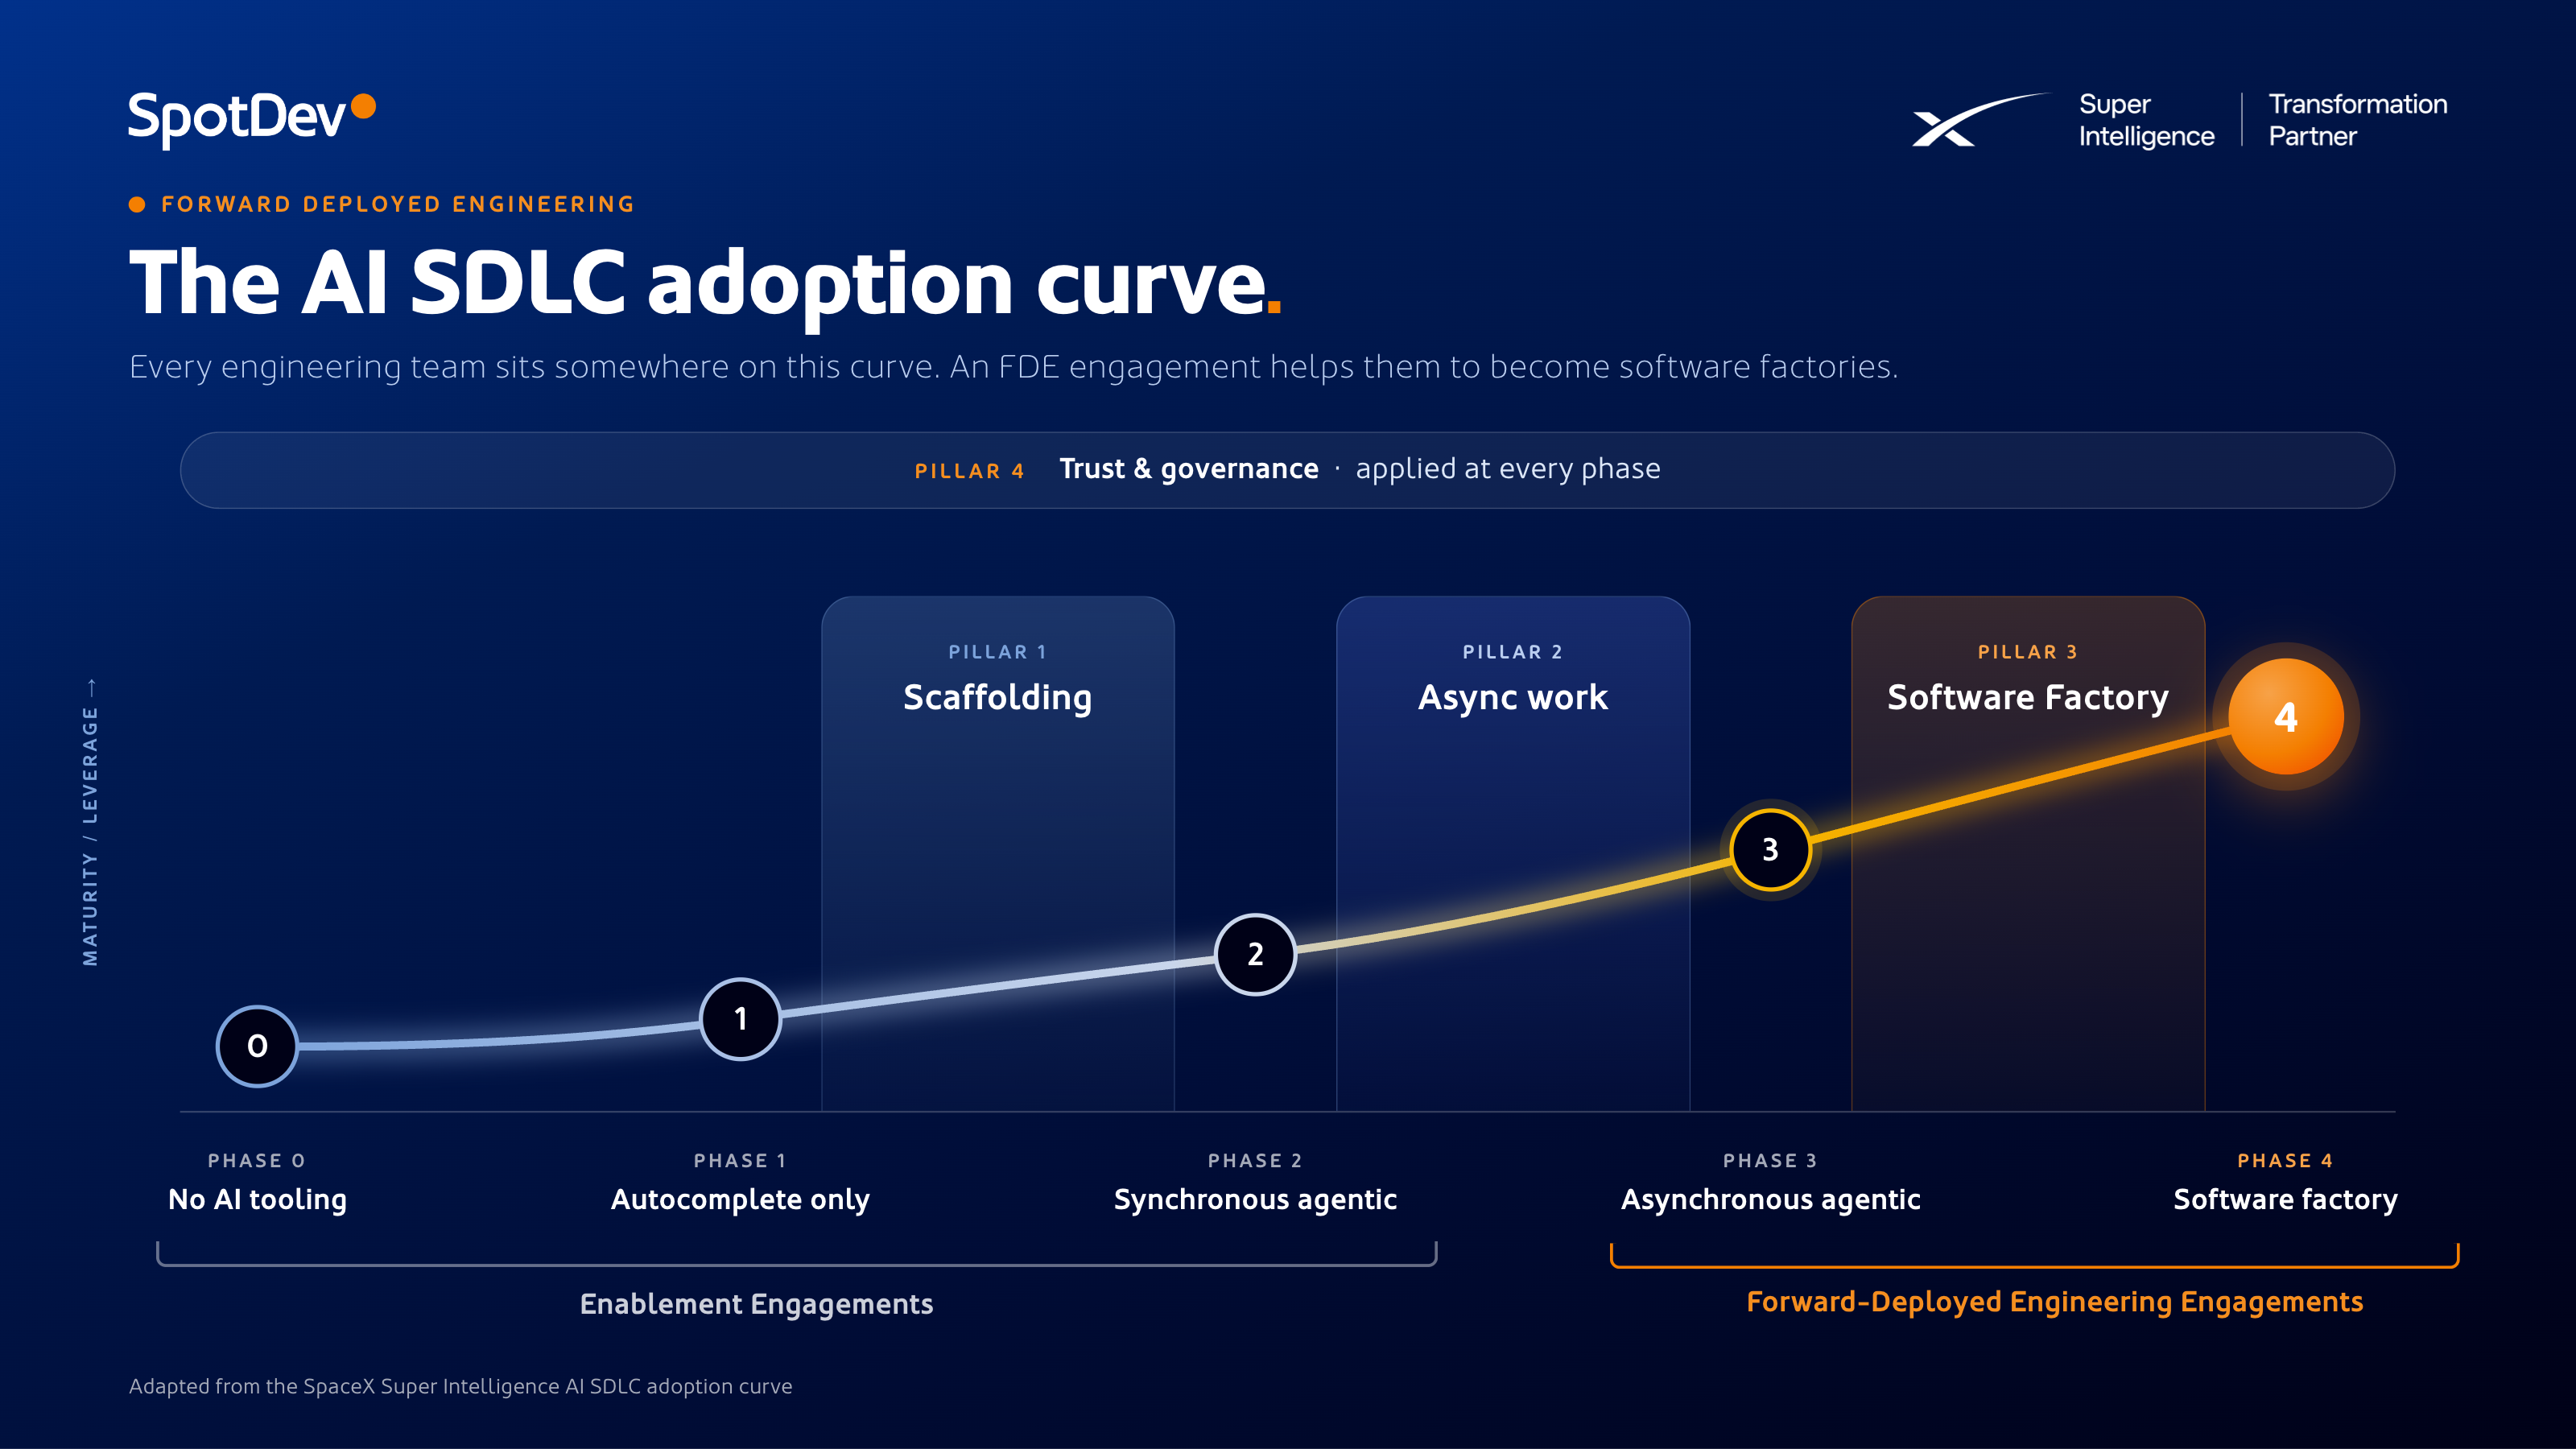
Buying Cursor seats is quick. Getting consistent, well-reviewed work out of those seats takes setup that a licence does not include: shared project rules and required team rules, team configuration kept in version control and shared through a team marketplace, a calibrated review process, a default model and spend set-up with agreed exceptions, and one named person who owns all of it. Put those in place first, check the team against a readiness test, and only then hand work to Cursor's cloud agents and automations.
One piece of context before the detail. Cursor announced on 14 Aug 2026 that it has been acquired by SpaceX, and it is now sold as part of The X Subscription from SpaceX Super Intelligence (SpaceXSI), the company behind Grok, which introduced that combined plan on 12 Oct 2026. Earlier plans continue for existing customers and some controls differ between them, so check which plan you are on. Our SpaceXSI guide for UK business explains how its products fit together.
Why licences on their own give broad, shallow use
A Carnegie Mellon study of open-source projects that adopted Cursor found a large but short-lived rise in development speed, concentrated in the first two months, alongside a lasting rise in static analysis warnings (up 30.3%) and code complexity (up 41.6%). The authors call for process changes that scale quality assurance with the faster pace. The study covers open-source repositories that mostly adopted Cursor between Aug 2024 and Mar 2025, before cloud agents.
A Microsoft study of command-line coding agents (Claude Code and GitHub Copilot CLI, written by Microsoft employees about their own company's rollout to its engineers) found that first use spread mainly through engineers' social networks, and the authors say visible peer use should be central to rollout. The DORA 2025 report describes AI as an amplifier of an organisation's existing strengths and weaknesses.
Cursor's Grab case study says Grab treated its rollout as enablement rather than a mandate, and that power users among its software engineers sent 18 times as many messages as light users. Our inference is that the same seat produced very different depth of use inside one company. Grab's route shows that setup-first is not the only way to roll Cursor out, though it is the order we recommend when cloud agents will work on shared code. Cursor's own enterprise admin setup guide covers identity, source control, company devices, optional organisations, teams and groups, and usage monitoring with alerts. It does not mention rules, marketplaces, model access or spend limits, so treat it as the floor.
The order we recommend
This sequence is our recommendation, drawn from how we use Cursor in our own engineering. Cursor does not publish it, but each step rests on what Cursor's documentation says the product does.
| Step | What to set up | Why it comes before cloud agents |
|---|---|---|
| 1. Shared rules | A few project rules in the repository, plus required team rules | Cloud agents read user, team and repository rules |
| 2. Versioned team configuration | Hooks, environment and approval settings committed, shared skills published, and a team marketplace for the shared set-up | Personal hooks and unsynced skills do not reach cloud agents |
| 3. Review calibration | Bugbot guidance and effort level, branch protection, and a decision on automated approval | A passing Bugbot check does not mean findings were resolved |
| 4. Spend controls and a default model | A team limit, alerts, a default model set-up, and agreement on who can change them | Cloud agents bill at API pricing for the chosen model |
| 5. A named owner | One person with Cursor's Admin role who is accountable for steps 1 to 4 | Later decisions about agents need someone with authority to make them |
1. Shared rules: small, owned and in the repository
Cursor has four kinds of rule. Project rules are stored in .cursor/rules and versioned with the code. Team rules are managed by admins from the Cursor dashboard on Team and Enterprise plans. Personal rules set in Cursor's settings are stored on the person's Cursor account and apply across all their projects. AGENTS.md is a plain markdown alternative. When guidance conflicts, team rules come first, then project rules, then personal rules.
Cursor advises starting small. Its Cursor Learn guide to customising agents says to add a rule only when the agent makes the same mistake repeatedly and to keep rules short, and its rules documentation says to keep rules under 500 lines and use a linter instead of copying a style guide. So the first job is the shared place, the owner and the change process, seeded with a handful of rules. One silent failure catches teams early: Cursor ignores a plain .md file in .cursor/rules because it has no frontmatter.
Team rules are where an admin sets conventions for everyone. An admin creates each one in the dashboard and chooses whether to enforce it. An enforced rule is required for every team member and cannot be switched off. A rule that is not enforced is on by default, but members can switch it off. Unticking "Enable this rule immediately" saves the rule as a draft that does not apply until it is enabled, which gives the owner a review step. Team rules are free text rather than files, can be limited to matching files with a glob, and apply to every conversation when no glob is set. Cursor's cloud agent best practices say they apply to all team members across every repository, cloud agents included.
Team rules are stored on Cursor's servers and sync to members, so they sit outside the repository. Our recommendation is to keep the text of every required team rule in a repository as well, so the owner has a change history and can review edits like code. We also advise enforcing only a handful. Cursor Learn notes that rules are included in every conversation, so they add up, and advises keeping them minimal and high quality.
Required means members cannot disable a rule. It does not mean the model obeys it. Cursor's safety and controls page calls rules "suggestions, not guarantees" and says to combine them with hooks for anything that must be followed, and its rules page adds that AI guidance should not be your only security control. Our guide to Cursor rules, skills, subagents and hooks covers how each mechanism works, and our post on AI coding governance for engineering teams sets the same questions out across vendors.
2. Versioned team configuration
Cloud agents work from what is in the repository and what has been synced or published, and a developer's laptop settings stay behind. Cursor does not copy personal or unsynced skills to cloud agents, synced skills stay private to the person who synced them, and admins can switch skill sync for cloud agents off for the whole team. To share a skill, publish it to the team marketplace.
The team marketplace is how an agreed set-up reaches the whole team. A plugin can package rules, skills, agents, commands, MCP servers and hooks into one bundle. Rules do not import from a repository on their own: Cursor's route is to package them in a plugin and publish it through a marketplace, which can import from GitHub, GitLab, Bitbucket and Azure DevOps. The settings an owner has to decide are below.
| Marketplace setting | What it does | Plan |
|---|---|---|
| Number of team marketplaces | Up to one on Teams, unlimited on Enterprise. On Enterprise only admins add them | Teams and Enterprise |
| Installation mode, per plugin | Default Off (developers choose whether to install), Default On (installed, but developers can opt out) or Required (always installed and cannot be uninstalled) | Teams and Enterprise |
| Allow members to publish | On by default, so members can publish skills to the Default marketplace. Turn it off and only admins can publish new skills. Installs are opt-in, so publishing a skill installs it for nobody else | Teams and Enterprise |
| Marketplace access | The whole team by default, and can be restricted to selected Organization Groups. Cursor's plan table shows no SCIM access gating on Teams | Group restriction on Enterprise |
| Allow Local Plugin Imports | Controls whether developers can import plugins locally. Off by default on Enterprise | Teams and Enterprise |
Our view is that Required keeps people on the agreed set-up, but Cursor does not describe it as a security control, and a plugin set to Default Off or Default On can be opted out of, so it is a weaker control than an enforced team rule. Plugins respect your MCP allowlist and blocklist, and Cursor manually reviews every plugin in its public Marketplace. That page speaks only of the public Marketplace, so our inference is that your own team marketplace gets no review from Cursor. The owner should review it like code, ideally through pull requests on the repository it imports from.
Two traps catch admins. Adding a Team MCP server to the Default marketplace does not install or enable it for every developer, and removing its marketplace entry, or deleting the marketplace, can delete the Team MCP server for local users and cloud agents. On Enterprise, adding a server to the MCP allowlist does not push it to anyone either: Cursor says to distribute an approved server through a team marketplace.
Hooks committed at .cursor/hooks.json run in cloud agents, and on Enterprise plans team and enterprise-managed hooks run there too. User-level hooks are not available in cloud agents. Environment configuration belongs in .cursor/environment.json, and command-approval settings can be committed per project or, where your plan includes the controls (Cursor's plan pages list auto-run controls under Enterprise), set centrally, where a team configuration overrides the project and user files. Cursor states on the run modes page that Auto-review is not a security boundary.
Two inferences of ours follow. A safety check that lives in someone's personal hooks file does not exist in a cloud run. And committed configuration is something an attacker can target: CVE-2025-54136, since fixed, described an attacker swapping an already-trusted MCP configuration in a shared repository for a malicious command. Review changes to .cursor files as you would code and keep Cursor up to date. Enterprise teams can also require approval before agents modify that directory.
3. Review calibration
Cloud agents open draft pull requests, and nothing merges until a person reviews the change. Cursor's own best-practice post spells out what that means: "The faster the agent works, the more important your review process becomes."
Bugbot reviews pull requests, but Cursor project rules do not apply to Bugbot runs. Its guidance goes in separate .cursor/BUGBOT.md files, so a team that writes conventions only in .cursor/rules will find the reviewer ignores them. Team admins can also create Bugbot team rules in Bugbot Automations, which apply to every repository on the team, with required rules prioritised over the rest. These are a separate set from the dashboard team rules in step 1, which apply only to Agent chat and not to Tab, Inline Edit or Bugbot, so a rule written for Agent does not reach the reviewer. Commenting bugbot run verbose=true on a pull request lists the rules a review used.
Effort levels on usage-based Bugbot plans set the trade between review cost and how much it may find. Requiring the Bugbot status check alone does not block merges on findings, because findings default to neutral, so branch protection needs a deliberate decision before agents start opening pull requests. Cursor's PR Routing & Approval can approve low-risk changes, and on Team plans every member can create and edit it, so decide who may switch on automated approval before anyone does.
Calibration means tuning Bugbot against the comments your senior reviewers already make and adding guidance where it misses what they catch. Our post on calibrating Bugbot to your senior reviewers goes further.
4. Spend controls and a default model
Each paid seat on the new plans includes a weekly usage pool, and on Teams seats do not share pools, so a few heavy cloud agent users can hit their own limits while colleagues' pools sit unused. Cloud agents are charged at API pricing for the selected model, and Cursor asks for a spend limit the first time someone uses them.
On Teams under The X Subscription, admins set one monthly additional usage limit for the whole team, either a fixed amount or an amount per seat, and only admins can change it. It caps additional usage: when someone reaches it, their paid additional usage stops and their included weekly usage keeps working. Enterprise adds member and group limits, which are always admin-only. Cursor's Teams pricing and Members pages also describe a default per-member limit on Teams, while its help centre, dashboard documentation and pricing page place member-level limits on Enterprise, so check your own dashboard before relying on one. Enforcement is not instant, and spend alerts warn without stopping anything. On legacy Teams and Enterprise plans, turn on the "Only Admins Can Edit Usage Settings" toggle, because while it is off any member can change these settings. Cursor's pricing page publishes no sterling prices, and its prices exclude VAT.
The default model works differently by plan. On Teams, the lever is Cursor Router's Impose Auto setting: Soft starts each new chat on Auto and lets members switch, and Hard locks the model picker to Auto. Both are off by default, and neither sets a named model. Workspace admins can also set a default model for cloud agents, used when a run does not specify one. On Enterprise, admins control which models members can use from a team baseline, and new models are opt-in rather than switched on for every enterprise team. Our post on Cursor spend controls and model choice covers router modes, pools and plan families in depth.
For exceptions, Cursor's own documented pattern on Enterprise is to keep strict defaults at the team level and use groups to widen access for selected cohorts. Groups can only widen. Model access is a union, so a person gets a model if the team or any of their groups allows it, and for spend the highest applicable limit applies. A group limit lower than a more permissive team setting does not tighten anyone's access. Our inference is that a cohort needing a tighter regime than the baseline, such as contractors, needs a stricter team baseline or a separate team, because a group cannot do it.
Cursor's docs use "groups" for three different things, so say which one you mean. Organization Groups are Enterprise cohorts that can span teams, and only organisation admins create them. Team directory groups set spend and policy within one team. Billing groups attribute spend for reporting and chargebacks and set no limits. Where groups come from your identity provider through SCIM, which is Enterprise only and needs SSO first, the identity provider decides who belongs and Cursor holds the settings: spend limits, model access and agent controls never sync from the directory.
Three admin traps are worth knowing. Raising the team-level spend limit only changes the default for people without a member or group override, so anyone with an override keeps their own limit until it is cleared. A strict model list can stop other features: when the allowed models leave Bugbot nothing it can use, the review stops and its check finishes as neutral. And groups can loosen security as well as cost, because for sandboxing the loosest setting wins. Cursor's pages do not agree on every combination of per-user, group and team limits, so test the effective limit with one pilot user before relying on it. Our guide to Cursor Enterprise admin, organisations, teams and groups sets out which setting wins in each case.
| Admin control | Teams | Enterprise |
|---|---|---|
| Team rules, optional or required | Yes | Yes |
| Default model | Impose Auto, which locks to Auto rather than a named model | Team model baseline, with the router configurable per Organization Group |
| Model access controls | No | Yes, with groups able to widen only |
| Team spend limit | One monthly additional usage limit, fixed or per seat, admin-only | Team, group and member limits, admin-only |
| Per-member limits | Cursor's pages disagree | Yes |
| Team marketplaces | Up to one | Unlimited |
| Marketplace access by group | No SCIM access gating | Restrict to selected Organization Groups |
| SCIM and Organization Groups | No | Yes, and SCIM needs SSO |
Basis: Cursor's plan comparison and the pages linked in this section.
5. A named owner
Cursor's role for this is Admin. Admins control team management and security settings, an unpaid Admin can manage the team without using a paid seat, and a team must always have at least one Admin and one paid member. Cursor also offers Free seats for IT, security or finance admins who manage Cursor without using it. "Owner" is our word: one named person with the Admin role who decides which team rules are required and when drafts are enabled, approves changes to committed configuration and marketplace content, decides whether members may publish to the marketplace and which plugins are Required, approves group exceptions and sets a date to review them, holds the spend limit and alerts, and settles settings such as automated approval and team follow-ups. Give them a second reviewer for configuration changes.
If you use organisations on Enterprise, team admin access does not grant organisation admin access, so decide who holds each role. Our Cursor Enterprise admin guide, linked above, covers the layers. Our guide to setting up Claude Code for a business team takes the same approach to ownership for teams on that tool.
Is the team ready for cloud agents? A test you can run
Cloud agents run in isolated virtual machines with full development environments, and they run terminal commands automatically. Cursor calls environment setup the most important step, and its best-practice page gives a plain test: "If it is hard for a human developer to test locally, it will also be hard for an agent." The checklist below is ours, built on Cursor's documentation.
| Check | Ready looks like | Basis |
|---|---|---|
| Local testability | The repository builds and runs its tests without services a cloud VM cannot reach | Cloud agent best practices |
| Environment | .cursor/environment.json is committed and works | Cloud agent setup |
| Source control access | An admin has connected source control, and users have read-write access to the repositories involved | Cloud agents |
| Team rules | Required team rules are agreed, enabled and also stored in a repository | Rules |
| Shared set-up | An approved team marketplace is in place and the publishing setting is decided | Plugins |
| Secrets | Secrets are scoped, with short-lived OIDC tokens in place of long-lived keys where possible | Security and network |
| Network | A decision on internet access, which is on by default and can be restricted to an allowlist | Cloud agent security |
| Team follow-ups | A decision on whether one user may steer an agent running with another user's secrets | Cloud agent settings |
| Review | Bugbot guidance is in place and branch protection requires a person | Bugbot |
| Seat tier | Developers are on a tier that includes cloud agents (Premium upwards on the new plans) | Models and pricing |
| Spend | A spend limit is set, someone receives the alerts and exceptions have a named approver | Spend limits |
| Owner | A named Admin is accountable for the settings above | Members and roles |
| Data | The security team has accepted that cloud agents store code | Privacy and data governance |
| Baseline | Usage analytics from the editor phase exist, read as a rough indicator of use | Usage analytics |
Signs a team is not ready yet
These signs come from our own experience rather than any vendor page, tied to the evidence above where it applies.
Use is uneven across teams. One team uses Cursor heavily and the team next to it barely opens it. The Microsoft study found that first use spread through peers, so a pilot group that others can watch working is a better lever than a mandate.
Senior engineers are sceptical. They usually carry the review load, and the Carnegie Mellon findings on warnings and complexity give their caution a basis. Their review comments are the material for Bugbot guidance and project rules, so bring them in early.
Every team is doing its own thing. Personal rules, unsynced skills and personal hooks do not reach cloud agents, so an agent working on shared code starts without the team's conventions. If nobody can say who administers the Cursor dashboard, that is the same sign.
Then automate
Cursor Automations run cloud agents on a schedule or in response to events from GitHub, GitLab, Slack, webhooks, Linear and other sources. Each automation runs as its own service account and does not use any member's personal usage, so the team spend limit is the control that matters. Cursor's master services agreement also says that for a feature labelled as executing code suggestions automatically without manual review, the customer is solely responsible for any impact, including putting safeguards, testing and monitoring in place. That is a point for your lawyers, and a good reason to finish steps 1 to 5 first. Our post on what to automate first with Cursor picks up from here.
UK points to settle before cloud agents
Cursor says cloud agents are the only feature that requires it to store code, and that if your security policy prohibits code storage you should not enable them. Cloud agents run in Privacy Mode, repository snapshots are deleted after 30 days of inactivity, and conversation history is kept indefinitely by default. On residency, Cursor offers US-only data residency to Enterprise customers and EU and UK inference-only coverage on request, with no UK storage option. The data processing addendum Cursor publishes includes the UK International Data Transfer Addendum but was last updated on 5 Nov 2025, before the change of ownership, so ask your lawyers to read the current documents. Our post on UK data residency across AI vendors sets this alongside the other providers.
Common questions
Do we need shared rules before rolling out Cursor to the whole team?
You need the shared place for them, an owner and a way to approve changes. The rules themselves can start small. Cursor advises adding a rule only when the agent repeats a mistake and keeping rules short and in version control. On Teams and Enterprise, an admin can mark a team rule as required so members cannot switch it off. Rules still guide the model and enforce nothing, so anything that must always happen belongs in hooks.
Who should own Cursor's team configuration?
One named person with Cursor's Admin role, which can be an unpaid admin seat, plus a second reviewer for changes to rules, hooks and marketplace content. That person also decides which team rules are required, who may publish to the team marketplace and who approves exceptions. Cursor's concept is the Admin role. Naming a single accountable owner is our recommendation.
How do we control Cursor spend across an engineering team?
Admins on Teams set one team-wide monthly additional usage limit, either a fixed amount or an amount per seat. Enterprise adds member and group limits, and where a person has limits from more than one source the highest applicable limit applies. Cursor's Teams pages disagree on whether Teams has per-member limits, so check your own dashboard. Alerts warn without stopping usage, and enforcement is not instant.
Do we need Enterprise to set a strict default model for a team?
Not for a default, but you do for a strict list. On Teams, Cursor Router's Impose Auto setting can lock the model picker to Auto, which is a default rather than a named model. Choosing which models members can use, and widening that for Organization Groups, is an Enterprise feature, and groups can only widen access beyond the team's baseline.
How do we share an agreed Cursor set-up across a team?
Publish it to a team marketplace, which Teams (up to one) and Enterprise (unlimited) include. Plugins there can carry rules, skills, MCP servers and hooks, and each can be set to Default Off, Default On or Required. On Enterprise, access can be restricted to Organization Groups. The owner should also decide whether members may publish skills there, which is on by default.
How do we know our team is ready for Cursor cloud agents?
Start with Cursor's own test: if the repository is hard for a person to build and test locally, it will be hard for an agent. Then check access, secrets, network policy, review, seat tier and spend limits, and confirm the security team accepts that cloud agents store code.
Should every developer get a Cursor seat on day one?
Our advice is to start with a pilot group that others can see working. The seat tier decides whether cloud agents are available at all, and on Teams each seat has its own usage pool.
If you want an outside view of where your team sits against the readiness test, start with our diagnostics. If you already know what you need, Request a Quote from our SpaceXSI and Cursor implementation page.
John Kelleher holds the SpaceX Super Intelligence Partner Network Accreditation: Forward Deployed Engineer, and the SpaceX Super Intelligence Technical Architect Accreditation.
Get new articles by email
Practical guides from the SpotDev team, when we publish them.
By submitting this form, you consent to us sending you emails with our latest content. Privacy Policy